AI governance that is audit-ready from day one
We assess how your organisation uses AI, write the policies and controls you need, and build governance into every AI system. Everything is aligned with Singapore's IMDA Model AI Governance Framework, the PDPA, the EU AI Act and ISO/IEC 42001.
- IMDA Model AI Governance Framework
- AI Verify
- PDPA
- EU AI Act
- GDPR and UK GDPR
- ISO/IEC 42001
- NIST AI RMF
Top AI-Powered Automation Agentic Solutions in APAC 2026
Named by CIOReview APAC after an evaluation by a panel of C-level executives, industry thought leaders and the editorial board, for governance-first agentic AI built on the GARD Framework.
Read the CIOReview feature ↗AI governance is no longer optional
Every organisation using AI, even only ChatGPT or Copilot, now needs a clear answer to one question: who controls it?
The EU AI Act has been in force since August 2024, with fines of up to €35 million or 7% of global turnover, and it reaches organisations outside the EU. Singapore's IMDA has published governance frameworks for traditional, generative and agentic AI.
Tenders, procurement questionnaires, partners and boards now ask how you govern AI. A documented answer builds trust and wins work.
Most AI risk comes from everyday tools used without a policy: personal data pasted into chatbots, answers used without checking, and no record of who did what.
Agentic AI can send messages, book meetings and change records. Without limits, human approvals and a kill switch, one mistake repeats at scale.
One comprehensive AI governance package
Everything your organisation needs to govern AI responsibly, in one standard package. It comes in two versions, depending on whether you have already built or adopted AI.
- An inventory of every AI tool and use case, including staff use of public AI tools
- Risk tiering for each use case under the IMDA framework and the EU AI Act
- A GARD readiness score and gap analysis against the IMDA framework, the PDPA and the EU AI Act
- An AI governance policy, an acceptable-use policy for staff and an approval process for new AI tools
- An AI risk register and impact assessments for priority use cases
- Human-oversight, data-protection (PDPA) and vendor due-diligence controls
- An evidence pack mapped to the IMDA framework, the EU AI Act and ISO/IEC 42001
- A prioritised roadmap presented to your leadership team, and a staff briefing
Two versions, one standard
For organisations that have built, bought or are already using AI solutions such as chatbots, agents, automations or AI features in their software.
- A review of every AI system that is live or in development
- Tests for the risks that matter: data leaks, wrong or biased answers, prompt injection and over-reach
- Missing controls added: human approvals, role-based access, decision logs and a kill switch for AI agents
- A remediation plan for each gap, in order of risk
- Monitoring set-up so behaviour, usage and cost stay visible
You get: Your existing AI brought under control, documented and defensible.
For organisations planning their first AI solutions that want to get governance right from day one.
- Use cases screened and risk-tiered before any money is spent
- Guardrails, approval rules and accountability agreed upfront
- Governance requirements written into vendor selection and system design
- A GARD-by-design blueprint for your first AI system
- A clear path to launch that is compliant from the start
You get: AI that is compliant from the first system, with no costly retrofitting.
Aligned with the frameworks that matter
We map your governance to Singapore's frameworks first, then to the international laws and standards your customers and partners follow.
Singapore's reference for responsible AI, now with editions for generative AI (2024) and agentic AI (2026).
How we cover it: Our assessment, policies and controls follow its sections: accountability, human involvement, operations and stakeholder communication.
Singapore's testing framework and toolkit for internationally recognised AI ethics principles.
How we cover it: We prepare the process checks and evidence used in AI Verify testing.
Personal data used in AI needs consent, purpose limits and protection, with PDPC guidance on AI systems.
How we cover it: We review data flows, consent and notification wording, retention and cross-border transfers.
A risk-based law with global reach. Uses in education, hiring and credit scoring are treated as high-risk.
How we cover it: We risk-tier every use case and document the transparency and oversight duties that apply.
The international standard for an AI management system.
How we cover it: Policies and records are structured to its controls, so certification later is easier.
The US framework to govern, map, measure and manage AI risk.
How we cover it: Your risk register follows the same four functions, which US partners recognise.
Read more: Singapore's IMDA AI governance framework, explained · The EU AI Act for Singapore businesses
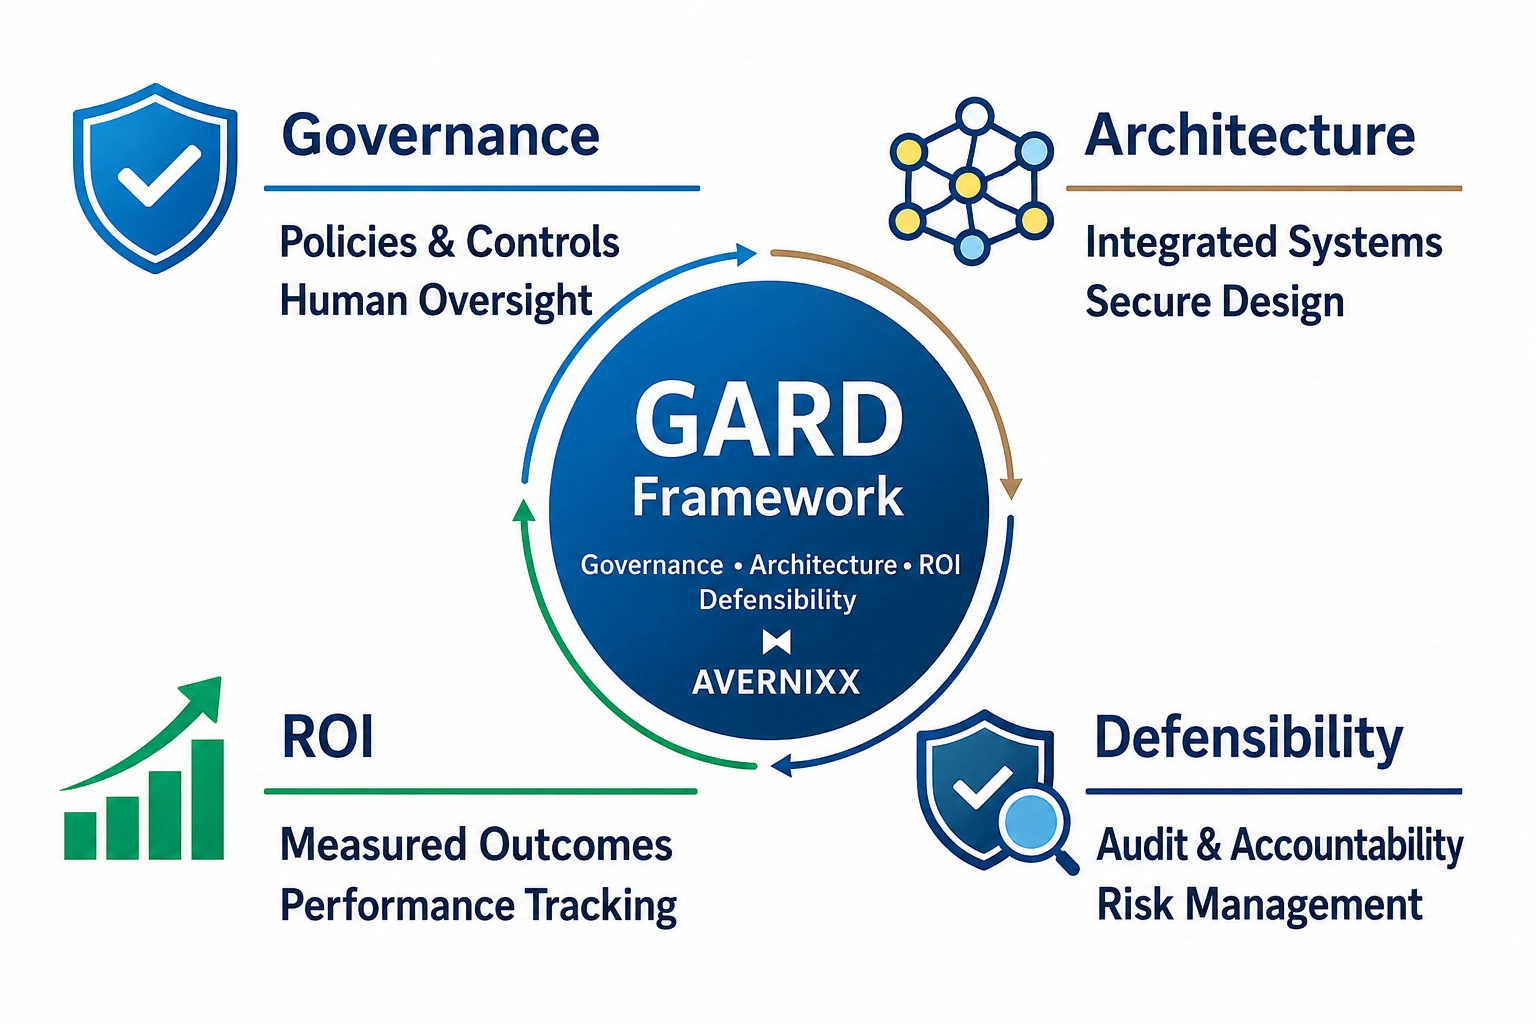
The GARD Framework
Every engagement and every AI system we build is checked against four pillars.
What the system can do, cannot do, and where human oversight is required, defined upfront.
Workflows reflect real operations, with controls embedded rather than bolted on.
Measurable outcomes and performance visibility tied to business value.
Audit trails, transparency and clear accountability, built to withstand scrutiny.
From first conversation to governed AI
We learn how you use AI today and agree the scope.
Inventory, risk tiering and a GARD readiness score.
Policies, risk register and controls written for your teams.
Staff briefing, approvals and controls built into your systems.
Regular reviews as your AI use and the rules change.
Not ready for a full engagement?
Start with our complimentary Introduction to AI Governance briefing: one hour for 3 to 10 of your leaders on the AI risks that matter, Singapore's guidance, the PDPA and key global rules. Attendees who pass a short knowledge check receive a digital certificate.
Scoped and quoted for your organisation
Pricing depends on how many AI tools and use cases you have, and whether your AI is already in place. You receive a fixed quotation after the consultation.
Frequently Asked Questions
Find out where your organisation stands on AI governance
A consultation takes 30 minutes. You leave with a clear view of your AI risks and the first steps to govern them.
Book an AI governance consultation